Free Open-Source
WireGuard® VPN Client
Unlock real, connection-level MFA the moment you pair it with Defguard free and open source.
Cross-platform, user-friendly UI. No CLI.
Windows
MacOS
Linux

Trusted by businesses across the globe
Security Specialist
Use any WireGuard® server today. Add the free, open-source Defguard server for connection-level MFA, Zero-Trust access.
DevOps / MSP
Manage any WireGuard® network from one client. Connect Defguard to add centralized management, MFA, and real-time.
WireGuard® User
Works with any WireGuard® configuration. Pair it with Defguard for one-tap biometric MFA and automatic config updates—for free.
Unlock the full potential of WireGuard® with effortless security and a seamless user experience.
Real, connection-level MFA - unique on the market
Unlike every other WireGuard® client, Defguard enforces MFA on the VPN connection itself. Combine biometric authentication, TOTP, or email verification with per-session pre-shared keys to protect every tunnel against stolen or reused credentials.
How WireGuard® VPN MFA works →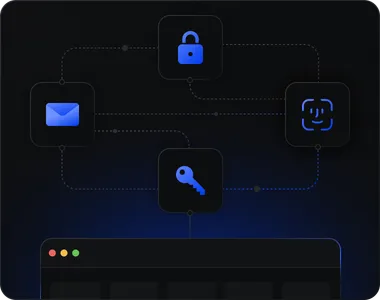
Biometric MFA for the tunnel
Approve a connection with Touch ID or Face ID instead of typing a code. You get frictionless, phishing-resistant authentication that protects the WireGuard® session itself - not just the login screen.
*This feature requires Open Source Defguard Server
Every instance, every location - one pane of glass
Manage multiple Defguard instances from a single client, each with its own VPN locations and users. Whether you're running separate environments or customer deployments, everything stays organized in one place.
Zero-touch provisioning
Deploy fully configured clients using a provisioning file, Active Directory/GPO, or Entra ID. Users install the client, sign in, and connect - without editing configuration files or copying credentials.
Self-hosted by design
Keep VPN keys and connection metadata on your own infrastructure while staying in full control of your deployment. Defguard is free, open source, developed in the EU, and built with security-first principles.
Connect to any standard WireGuard® server without changing your existing setup.
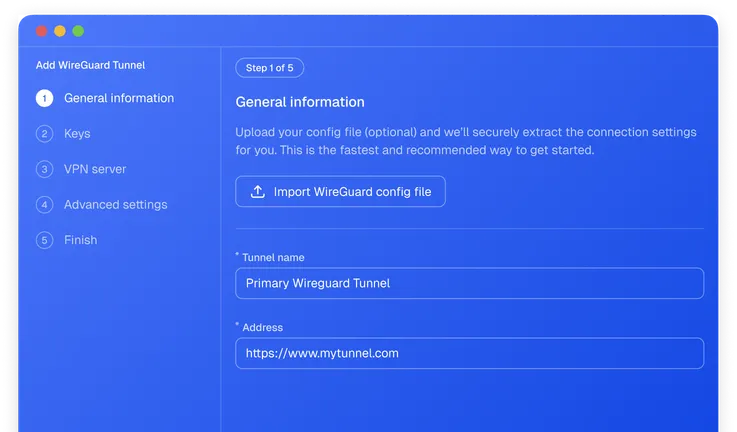
Get the most out of WireGuard® with advanced Enterprise features.
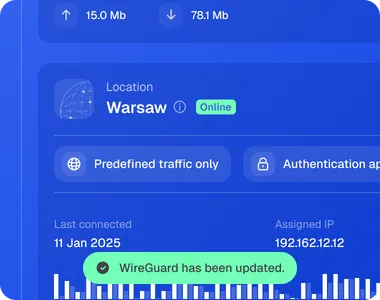
Real-time configuration sync
Keep every client up to date automatically. Changes to VPN locations, DNS settings, or access policies are applied in seconds, without re-importing configurations or asking users to take any action.
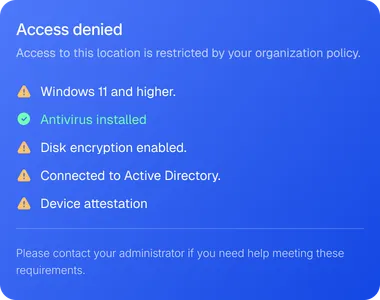
Device Policy Posture
Verify the device before allowing a VPN connection. Enforce requirements like domain membership, disk encryption, antivirus protection, OS updates, and client version to block non-compliant endpoints.
Coming in 2.2
Device Attestation
Verify that every connection comes from a genuine, trusted device. Hardware-backed identity prevents cloned, spoofed, or unauthorized machines from accessing your network—even with valid credentials.
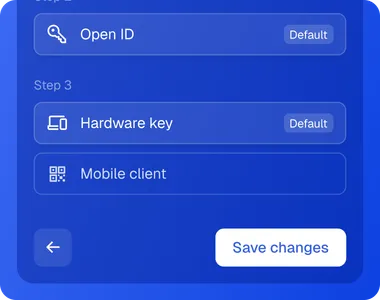
Redesigned for a faster and intuitive experience across every platform.
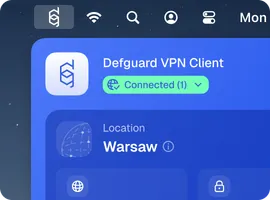
Tray Mode
Connect, disconnect, and switch VPNs directly from the system tray. Everyday tasks stay just one click away.
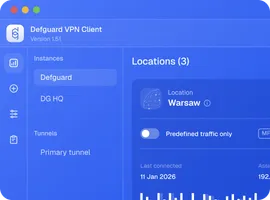
Full Desktop
Switch to the full desktop interface for advanced settings, detailed connection information, and extra configuration options.
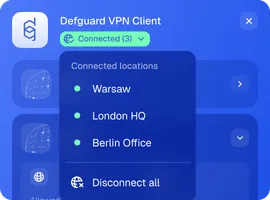
Multiple Connections
Manage all your WireGuard® connections in one place. Switch between servers and locations in just a few clicks.
Can I self-host my own WireGuard® VPN server?
Yes. WireGuard® is a protocol, not a service — you run the server on your own infrastructure and connect to it with a compatible client. Nothing is routed through third-party infrastructure and no external party holds your keys or connection data.
Defguard is built to be deployed on-premise or in your own cloud tenancy, with all identity, keys, ACLs and logs staying inside your environment. This is what makes it viable for regulated sectors and organisations with data sovereignty or NIS2 obligations.
Does WireGuard® support SSO login with Okta, Entra ID or Google?
Not on its own. WireGuard® authenticates devices by public key only — it has no concept of users, identity providers or login sessions. SSO has to be added by the platform managing the tunnels.
Defguard integrates with external identity providers over OpenID Connect (OIDC), so users authenticate with your existing IdP before a connection is established:
Defguard also works as an OIDC provider itself if you don’t already run one.
Does WireGuard® support MFA (2FA)?
Not natively. The protocol authenticates peers cryptographically by keypair, with no second factor. Most WireGuard®-based products advertising MFA only apply it to the admin panel login or the initial client setup — the tunnel itself stays protected by a static key file.
Defguard enforces MFA at the connection layer using rotating pre-shared keys, so every connection attempt requires a second factor:
A stolen private key alone is not enough to connect.
Is there a WireGuard® client for iOS and Android?
Yes. Defguard Client is available for iOS on the App Store and for Android on Google Play, alongside the Windows, macOS and Linux desktop builds.
Mobile clients support the same enrollment flow and MFA methods as desktop, including biometric authentication. An enrolled phone can also act as the second factor for a desktop connection.
Note that the iOS and Android apps connect to a Defguard server — unlike the desktop clients, they are not intended for standalone use with a manually imported configuration file.
What is the best WireGuard® client for macOS?
For a single personal tunnel the official app is fine. For a team, you want a client that handles enrollment, central configuration updates and access revocation — otherwise every network change means distributing new .conf files by hand.
Defguard Client for macOS bundles wireguard-go and has no external requirements, and is available directly or via Homebrew. It syncs configuration automatically from your self-hosted Defguard instance and supports connection-level MFA including TouchID/FaceID through the mobile app.
Do I need the official WireGuard® app to use a WireGuard® client on Windows?
No. Defguard Client is fully self-contained on Windows — it uses a native WireGuardNT-based networking implementation rather than shelling out to the official WireGuard® tools. Download the MSI, install it, and the tunnel is managed in-process.
That also means no external dependency to package around when deploying via Intune or GPO, and no second application to keep patched. If you already have the official WireGuard® app installed, you can leave it in place — the two coexist without conflict, so there’s nothing to uninstall before migrating.
How do I revoke WireGuard® access for a lost or stolen device?
With plain WireGuard® you have to edit the server configuration and remove the peer’s public key by hand, then reload the interface — on every server that device could reach.
In Defguard an administrator disables the device or user in the admin panel and access stops centrally. On MFA-enabled locations the device also loses its session pre-shared key, so a copied key file on the lost machine can’t re-establish a connection.
Can I deploy the WireGuard® client via Intune, GPO or MDM?
Yes. Defguard Client ships as an MSI package on Windows for distribution through Microsoft Intune, Active Directory GPO or standard package managers, and the macOS client is distributed via the Mac App Store, which allows push to managed machines through MDM/UEM tooling and handles updates automatically.
For zero-touch provisioning, all clients support file-based enrollment configuration — the enrollment token and URL are read at first launch, so administrators can preconfigure endpoints using whichever distribution tool they already run. Users get a working, correctly configured VPN client without touching a config file or contacting IT.
Does WireGuard® work on restrictive networks that block VPN traffic?
Usually, but not always. WireGuard® runs over UDP only, so networks that block or heavily restrict UDP will block the tunnel. This is a protocol-level constraint, not a client limitation — no WireGuard® client can work around a network that drops all UDP.
In practice most restrictive networks are far more permissive on UDP port 443, which carries QUIC and HTTP/3 traffic, so running the VPN endpoint on that port resolves the majority of cases. Where a network permits only TCP, a TLS-based protocol such as OpenVPN over TCP 443 remains more reliable. It is worth knowing this before a rollout rather than discovering it from a user in an airport.
Is WireGuard® secure enough for enterprise use?
Yes. WireGuard® uses a fixed, modern cryptographic suite based on the Noise protocol framework, with no configurable weak ciphers to misconfigure. Its codebase is roughly 4,000 lines against OpenVPN’s 100,000+, which makes independent audit genuinely feasible, and it has been part of the Linux kernel since version 5.6.
The protocol is only half the question in an enterprise context. WireGuard® on its own has no users, no groups, no MFA and no revocation — those come from the platform managing it. Defguard is written in Rust for memory safety, publishes its security audit results and daily CVE/SBOM reports, and is developed under an ISO/IEC 27001:2022 certified process.
Do I need a paid license to use the Defguard WireGuard® client?
No. Defguard Client is free and open source on every platform — Windows, macOS, Linux, iOS and Android. There is no subscription, no account requirement and no per-device fee for the client itself.
A license applies only to the self-hosted Defguard server, and only past the free tier: